Menu

Show posts

This section allows you to view all posts made by this member. Note that you can only see posts made in areas you currently have access to.

Show posts Menu

Topics - Timeraider

#1
26.7 Series / 26.7.3_2 Kernel panic - missing init
August 28, 2026, 01:55:07 PM
That cant be good.. image speaks for itself XD
Wont be the best strart of the weekend ive had.. not sure how ill fix it yet

#2
nginx plugin -> security header UI not working since 26.7
So under the Nginx plugin -> configuration -> http(s), you have an option for Security headers.
Once I try editing any of them, the UI acts weird and while it shows the tabs it refuses to show any content.
Makes it impossible to update it.
This kinda blocks me from fixing one of my sites XD

#3
nginx itself works and the other pages also work, but specifically the configuration page (arguably the most important) crashes.
Errors:
[16-Jul-2026 11:51:36 Europe/Amsterdam] TypeError: count(): Argument #1 ($value) must be of type Countable|array, null given in /var/lib/php/cache/_usr_local_opnsense_mvc_app_views_layout_partials_base_form.volt.php:9
Stack trace:
#0 [internal function]: Phalcon\Mvc\View\Engine\Volt->render('/usr/local/opns...', Array, false)
#1 [internal function]: Phalcon\Mvc\View->engineRender(Array, 'layout_partials...', false, false)
#2 [internal function]: Phalcon\Mvc\View->partial('layout_partials...', Array)
#3 /var/lib/php/cache/_usr_local_opnsense_mvc_app_views_layout_partials_base_tabs_content.volt.php(8): Phalcon\Mvc\View\Engine\AbstractEngine->partial('layout_partials...', Array)
#4 [internal function]: Phalcon\Mvc\View\Engine\Volt->render('/usr/local/opns...', Array, false)
#5 [internal function]: Phalcon\Mvc\View->engineRender(Array, 'layout_partials...', false, false)
#6 [internal function]: Phalcon\Mvc\View->partial('layout_partials...', Array)
#7 /var/lib/php/cache/_usr_local_opnsense_mvc_app_views_opnsense_nginx_index.volt.php(267): Phalcon\Mvc\View\Engine\AbstractEngine->partial('layout_partials...', Array)
#8 [internal function]: Phalcon\Mvc\View\Engine\Volt->render('/usr/local/opns...', Array, true)
#9 [internal function]: Phalcon\Mvc\View->engineRender(Array, 'OPNsense/Nginx/...', true)
#10 /usr/local/opnsense/mvc/app/controllers/OPNsense/Base/ControllerBase.php(151): Phalcon\Mvc\View->processRender('', '')
#11 /usr/local/opnsense/mvc/app/library/OPNsense/Mvc/Dispatcher.php(168): OPNsense\Base\ControllerBase->afterExecuteRoute(NULL)
#12 /usr/local/opnsense/mvc/app/library/OPNsense/Mvc/Router.php(156): OPNsense\Mvc\Dispatcher->dispatch(Object(OPNsense\Mvc\Request), Object(OPNsense\Mvc\Response), Object(OPNsense\Mvc\Session))
#13 /usr/local/opnsense/mvc/app/library/OPNsense/Mvc/Router.php(139): OPNsense\Mvc\Router->performRequest(Object(OPNsense\Mvc\Dispatcher))
#14 /usr/local/opnsense/www/index.php(66): OPNsense\Mvc\Router->routeRequest('/ui/nginx', Array)
#15 {main}


Already did the obvious like reinstalling nginx plugin, restarting etc.
#4
Not gonna say I dont trust Zenarmor updates.. but if I have my network and selected the correct devices as trusted and afterwards ill turn on block connection for all untrusted devices.
What is best practise to make sure that if Zenarmor somehow clears the Trusted list, I still have a way into my router outside of physically connecting a screen to it :P
#5
EDIT:

Ok.. so "parameters" going to %s only means 1 word goes to %s, not all of it. And if your %s's in the configd is lower than the amount of words filled it, it simply doesnt work. You can have more %s's than parameters and it will still work though.

So all I had to do was adjust the configd and change it to
[test.dyndns]
command:/scripts/test.sh
parameters:%s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s %s
type:script_output
message: Running dynamic DNS check on domain
description: Run dynamic DNS check on domain


ORIGINAL:

So.. basically to facilitate some dynamic dns for me which cant get through the plugin .. I made myself a bash script that doesn exactly as I want.
Now I am incorporating it into the cron job interface in OPMSense, but its not exactly working as planned.
Basically.. (some of these will be templates and not my actual setup, but its the same idea.
/scripts holds an script (lets say test.sh) that checks IPs and then changing my DNS names through Directadmin .. this script works as I can run it manually as well as through cron and it works like that.
However, I want to make it so that I can edit my cron job so I can always change which subdomains it updates through the UI and not have it hardcoded in the script
If I run the command "test.sh test test2" in the CLI .. it works, updating those 2 subdomains.. meaning the parameters do work.


However... if I set it up as shown above and then have this as configd .. it doesnt work

[test.dyndns]
command:/scripts/test.sh
parameters:%s
type:script_output
message: Running dynamic DNS check on domain
description: Run dynamic DNS check on domain


So basically.. If I hardcode the subdomains, it works manually and through the webui Cron
If I parameter the subdomains it works manually, doesnt work through webui Cron (and only thing I change in the configd is at parameters I add %s
Anyone has any idea?
#6
Edit: Solved.. sorta. Issue found!
After doing more testing I found out my issue was that the opnsense had issues retrieving geo ip for a geolocation block rule. This started happening after last update.
Somehow this made it so that it blocked all countries instead of the ones I set up in the settings.
Disabling that rule allows my reverse proxies to work untill I fix or find the cause of the geo ip issue

Issue:
Using the nginx plugin in which ive made a good few http servers -> Location and then the 2 upstream parts.. default reverse proxies
My reverse proxies are not able to be reached anymore by domain URLs. Neither form the outside nor the inside.
The only way it does work from the INSIDE is to put domains in Unbound DNS Overrides and refer them to any of my LAN interface gateways.
Firewall does not show any blocks, neither does Zenarmor.
Everything worked fine (domains were reachable from outside as well as inside my network simply with  the nginx plugin) at 24.7_9 .. only after 24.7.1 it stopped working.
There is nothing in front of my OPNsense.

Any ideas?
#7
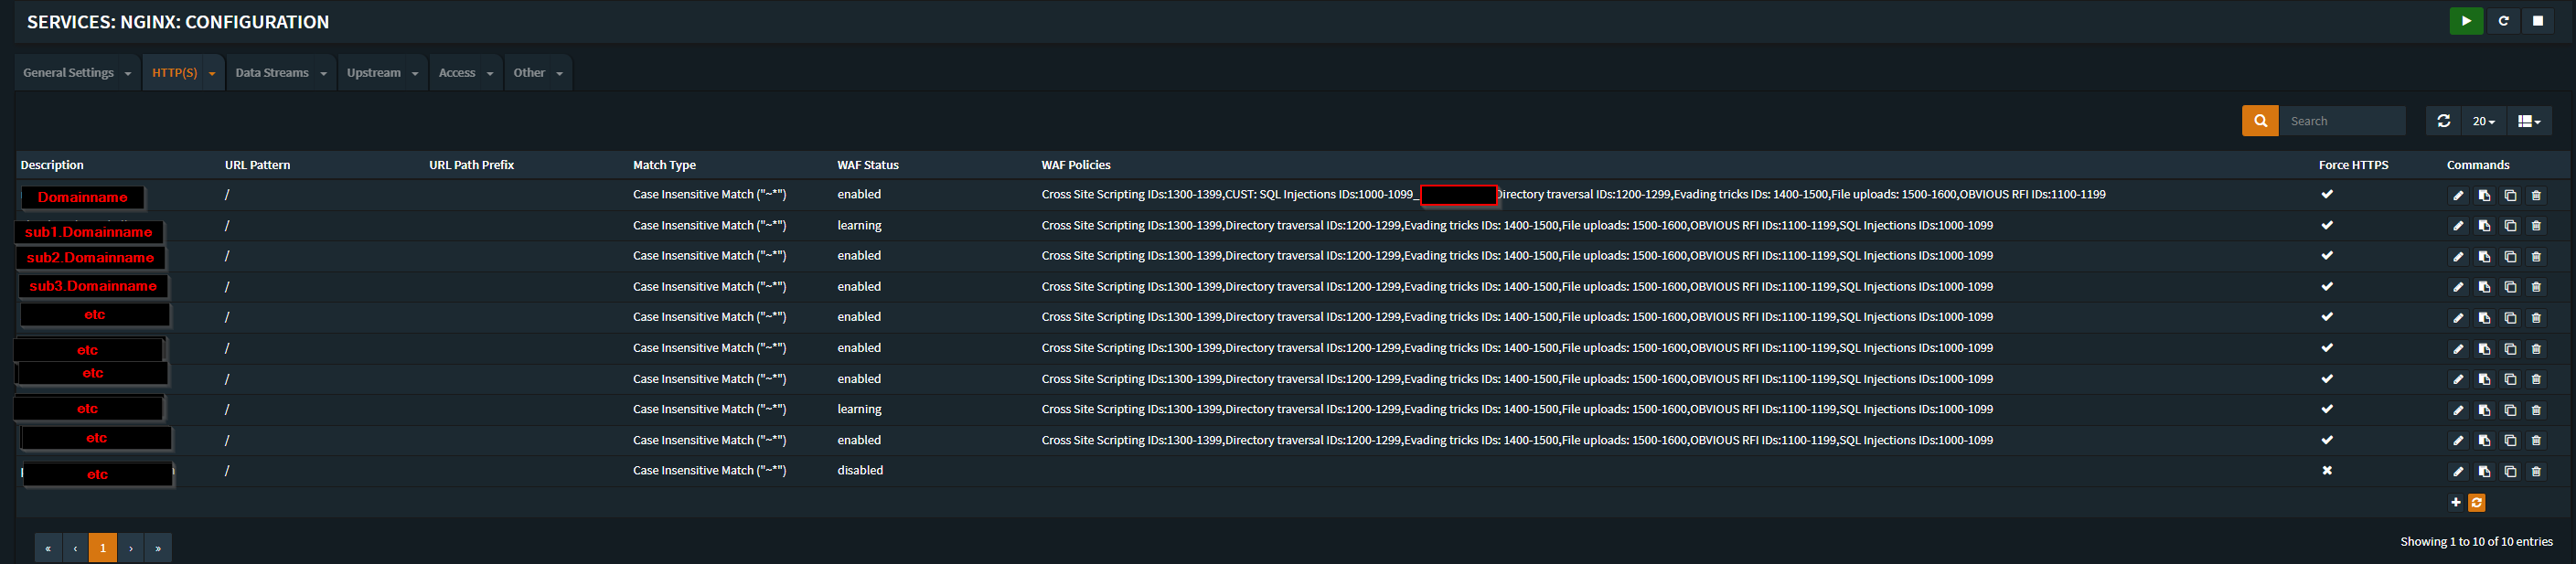
So.. basically I have my nginx like this. Simple reverse proxy for a main website that is the domainname and then a few sites that contain a subname.domainname... nothing special.


Now I have been turning on and editing WAF policies to make sure its all fully secured, but im walking against an issue.
WAF policies active on the main domain name are blocking stuff happening on the subdomainnames within nginx.

So lets say it like this.. sub2.domainname.com has issues with something due to the SQL injections policy of WAF. I then turn off only the SQL injections policy for sub2.domainname.com. It still gets blocked.
However when I then also turn off the SQL injections policy on the domainname, it works.
In the logging I can see that rules/policies only active on the domainname site also seem to block stuff on the subdomains.

How can I try to seperate it so that WAF rules from the main site dont affect the subdomains (which are totally seperate sites)?
#8
Good day,

There is no doubt that I am doing something wrong, but I would like to figure it out.
I used to use the reverse proxy on my Synology NAS which basically was an extremely simple UI whereby you point 1 thing to another :P
Due to the fact that im setting up some services on another device as well I imagined the best way to handle this is  reverse proxy it from the router.

Now.. ive used the tutorials online to at least set up a basic setup, however I am running into an annoying issue already. Even though at http server ive got the servername set to aaa.domain.com, it also proxies domain.com, bbb.domain.com etc. etc. so basically.. all the other subdomains as well.

My setup right now looks like this:
httpserver


location:


Upstream:


Upstream server:


traffic stats screen:


firewall rule:


I also have Unbound set up with all the subdomains so I could access them from inside LAN. Not sure if that influences anything.

So basically wondering why its proxying more than im telling it to?

Any general tips on setting it up with a good few subdomains that will need to be directed to different IPs would be appreciated as well.

If I figure anything out in the meantime ill be sure to update.