
 "
Hello.
I am trying to establish an IPsec IKEv2 connection to a VPN provider. So far without success.
Here is my configuration:
- Add IPsec Rules to Firewall->Rules->WAN
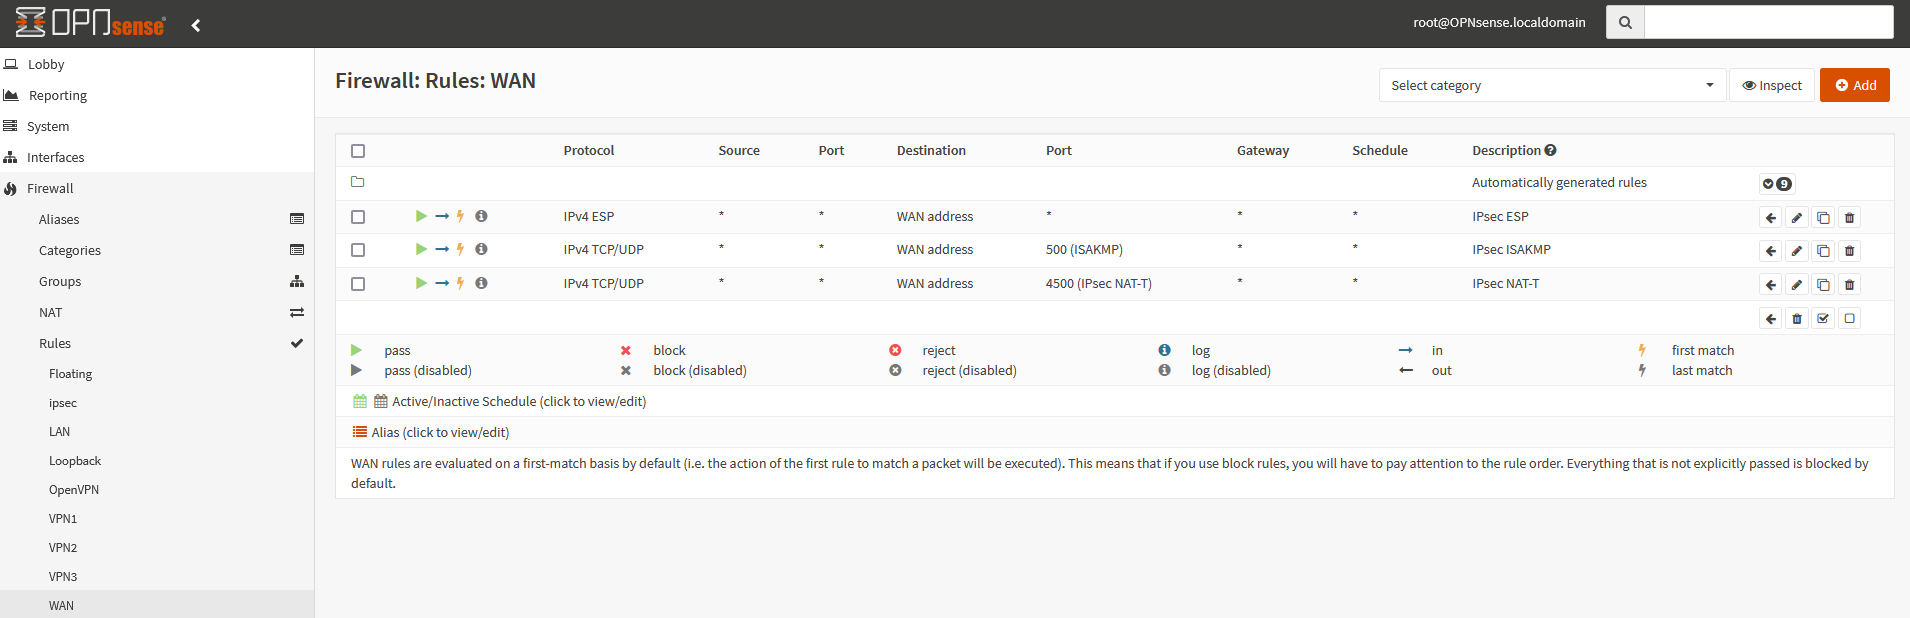
- Enable IPsec
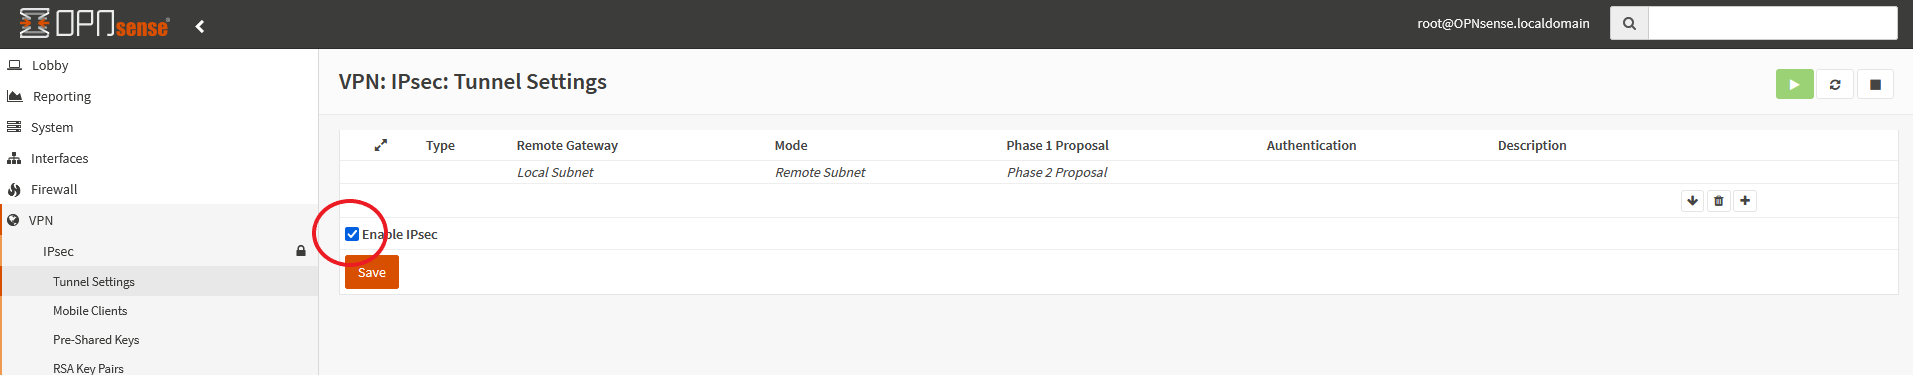
/usr/local/etc/ipsec.opnsense.d/ipsec.conf
/usr/local/etc/ipsec.secrets.opnsense.d/ipsec.secrets
Then start IPsec
Here is the log:
- After that I made a backup and added an interface:
- Finally I have imported the backup (interface).
Then I have created a gateway under System-> Gateways-> Single

-Firewall->Rules->LAN configured
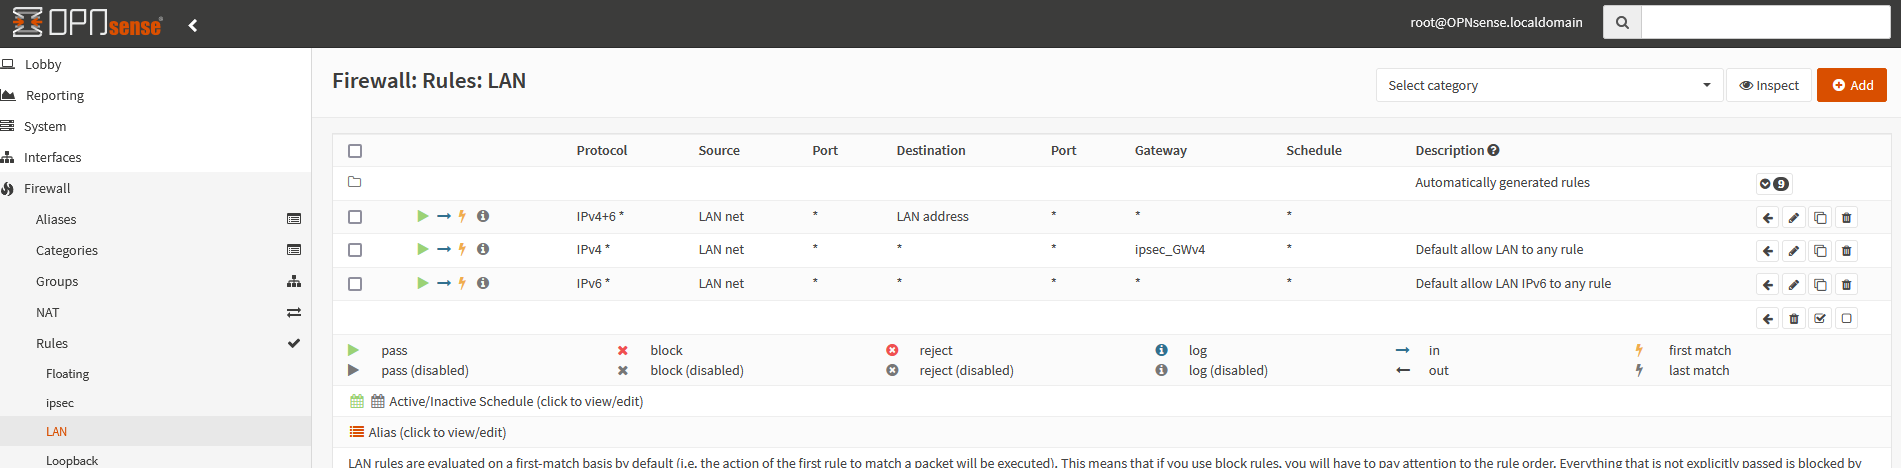
-Firewall->NAT-> Outbound Rule added
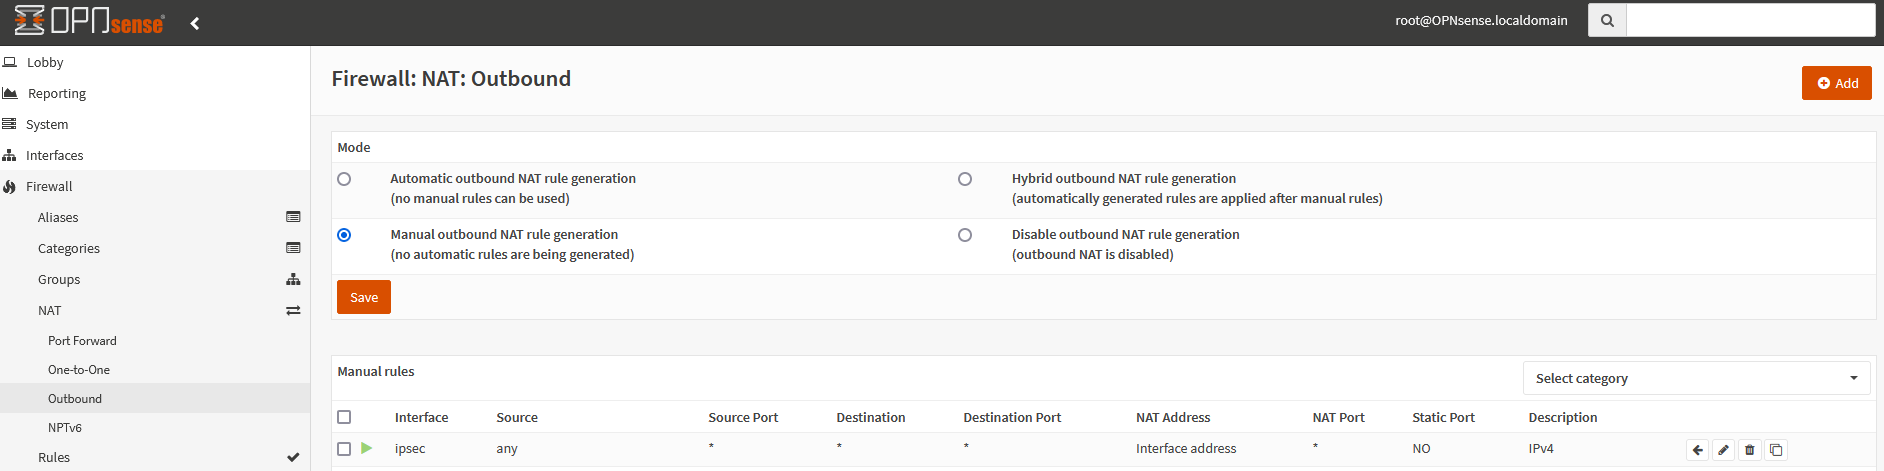
In the end, it was always indicated that the website is not secure.
Can anyone help?
I am trying to establish an IPsec IKEv2 connection to a VPN provider. So far without success.
Here is my configuration:
- Add IPsec Rules to Firewall->Rules->WAN

- Enable IPsec

/usr/local/etc/ipsec.opnsense.d/ipsec.conf
Code Select
config setup
	charondebug="all"
	uniqueids=never

conn lan-passthrough
	leftsubnet=192.168.2.0/24 # Replace with your LAN subnet
	rightsubnet=192.168.2.0/24 # Replace with your LAN subnet
	authby=never # No authentication necessary
	type=pass # passthrough
	auto=route # no need to ipsec up lan-passthrough

conn PP
	eap_identity="username"
	type=tunnel
	mobike=no
	keyexchange=ikev2
	keyingtries=%forever
	dpdaction=restart
	closeaction=restart
	compress=no
	dpddelay=300s
	inactivity=36000s
	rekey=no
	forceencaps=yes
	authby=secret
	ike=aes256-sha256-modp2048
	esp=aes256-sha256
	leftfirewall=yes
	left=192.168.2.1
	leftid=192.168.2.1
	leftsourceip=%config4
	leftsendcert=never
	leftauth=eap-mschapv2
	rightfirewall=yes
	rightauth=pubkey
	right=37.48.94.1
	rightid=%any
	rightsubnet=0.0.0.0/0
	rightsendcert=always
	auto=add
/usr/local/etc/ipsec.secrets.opnsense.d/ipsec.secrets
Code Select
# /etc/ipsec.secrets - strongSwan IPsec secrets file

username : EAP "password"
Then start IPsec
Code Select
ipsec up PPHere is the log:
Code Select
root@OPNsense:~ # ipsec up PP
no files found matching '/usr/local/etc/strongswan.opnsense.d/*.conf'
initiating IKE_SA PP[1] to 37.48.94.1
generating IKE_SA_INIT request 0 [ SA KE No N(NATD_S_IP) N(NATD_D_IP) N(FRAG_SUP) N(HASH_ALG) N(REDIR_SUP) ]
sending packet: from 192.168.2.1[500] to 37.48.94.1[500] (1028 bytes)
received packet: from 37.48.94.1[500] to 192.168.2.1[500] (38 bytes)
parsed IKE_SA_INIT response 0 [ N(INVAL_KE) ]
peer didn't accept DH group MODP_2048, it requested CURVE_25519
initiating IKE_SA PP[1] to 37.48.94.1
generating IKE_SA_INIT request 0 [ SA KE No N(NATD_S_IP) N(NATD_D_IP) N(FRAG_SUP) N(HASH_ALG) N(REDIR_SUP) ]
sending packet: from 192.168.2.1[500] to 37.48.94.1[500] (804 bytes)
received packet: from 37.48.94.1[500] to 192.168.2.1[500] (265 bytes)
parsed IKE_SA_INIT response 0 [ SA KE No N(NATD_S_IP) N(NATD_D_IP) CERTREQ N(FRAG_SUP) N(HASH_ALG) N(CHDLESS_SUP) N(MULT_AUTH) ]
selected proposal: IKE:AES_GCM_16_256/PRF_HMAC_SHA2_512/CURVE_25519
local host is behind NAT, sending keep alives
received cert request for "C=CH, ST=Zug, L=Zug, O=Perfect Privacy, CN=Perfect Privacy IPSEC CA, E=admin@perfect-privacy.com"
sending cert request for "C=CH, ST=Zug, L=Zug, O=Perfect Privacy, CN=Perfect Privacy, E=admin@perfect-privacy.com"
sending cert request for "C=CH, ST=Zug, L=Zug, O=Perfect Privacy, CN=Perfect Privacy IPSEC CA, E=admin@perfect-privacy.com"
establishing CHILD_SA PP{1}
generating IKE_AUTH request 1 [ IDi CERTREQ CPRQ(ADDR DNS) N(ESP_TFC_PAD_N) SA TSi TSr N(MULT_AUTH) N(EAP_ONLY) N(MSG_ID_SYN_SUP) ]
sending packet: from 192.168.2.1[4500] to 37.48.94.1[4500] (398 bytes)
received packet: from 37.48.94.1[4500] to 192.168.2.1[4500] (1248 bytes)
parsed IKE_AUTH response 1 [ EF(1/2) ]
received fragment #1 of 2, waiting for complete IKE message
received packet: from 37.48.94.1[4500] to 192.168.2.1[4500] (518 bytes)
parsed IKE_AUTH response 1 [ EF(2/2) ]
received fragment #2 of 2, reassembled fragmented IKE message (1701 bytes)
parsed IKE_AUTH response 1 [ IDr CERT AUTH EAP/REQ/ID ]
received end entity cert "C=CH, O=Perfect Privacy, CN=amsterdam4.perfect-privacy.com"
  using certificate "C=CH, O=Perfect Privacy, CN=amsterdam4.perfect-privacy.com"
  using trusted ca certificate "C=CH, ST=Zug, L=Zug, O=Perfect Privacy, CN=Perfect Privacy IPSEC CA, E=admin@perfect-privacy.com"
checking certificate status of "C=CH, O=Perfect Privacy, CN=amsterdam4.perfect-privacy.com"
certificate status is not available
  reached self-signed root ca with a path length of 0
authentication of 'amsterdam.perfect-privacy.com' with RSA_EMSA_PKCS1_SHA2_256 successful
server requested EAP_IDENTITY (id 0x00), sending 'username'
generating IKE_AUTH request 2 [ EAP/RES/ID ]
sending packet: from 192.168.2.1[4500] to 37.48.94.1[4500] (75 bytes)
received packet: from 37.48.94.1[4500] to 192.168.2.1[4500] (97 bytes)
parsed IKE_AUTH response 2 [ EAP/REQ/MSCHAPV2 ]
server requested EAP_MSCHAPV2 authentication (id 0xB3)
generating IKE_AUTH request 3 [ EAP/RES/MSCHAPV2 ]
sending packet: from 192.168.2.1[4500] to 37.48.94.1[4500] (129 bytes)
received packet: from 37.48.94.1[4500] to 192.168.2.1[4500] (134 bytes)
parsed IKE_AUTH response 3 [ EAP/REQ/MSCHAPV2 ]
EAP-MS-CHAPv2 succeeded: 'Welcome2strongSwan'
generating IKE_AUTH request 4 [ EAP/RES/MSCHAPV2 ]
sending packet: from 192.168.2.1[4500] to 37.48.94.1[4500] (67 bytes)
received packet: from 37.48.94.1[4500] to 192.168.2.1[4500] (65 bytes)
parsed IKE_AUTH response 4 [ EAP/SUCC ]
EAP method EAP_MSCHAPV2 succeeded, MSK established
authentication of '192.168.2.1' (myself) with EAP
generating IKE_AUTH request 5 [ AUTH ]
sending packet: from 192.168.2.1[4500] to 37.48.94.1[4500] (129 bytes)
received packet: from 37.48.94.1[4500] to 192.168.2.1[4500] (253 bytes)
parsed IKE_AUTH response 5 [ AUTH CPRP(ADDR DNS DNS) SA TSi TSr ]
authentication of 'amsterdam.perfect-privacy.com' with EAP successful
IKE_SA PP[1] established between 192.168.2.1[192.168.2.1]...37.48.94.1[amsterdam.perfect-privacy.com]
installing DNS server 37.48.94.55 via resolvconf
installing DNS server 31.204.152.232 via resolvconf
installing new virtual IP 10.4.74.138
created TUN device: tun0
selected proposal: ESP:AES_CBC_256/HMAC_SHA2_256_128/NO_EXT_SEQ
CHILD_SA PP{1} established with SPIs c18395de_i c83adaf6_o and TS 10.4.74.138/32 === 0.0.0.0/0
updown: /usr/local/libexec/ipsec/_updown: iptables: not found
updown: /usr/local/libexec/ipsec/_updown: iptables: not found
updown: /usr/local/libexec/ipsec/_updown: iptables: not found
updown: /usr/local/libexec/ipsec/_updown: iptables: not found
connection 'PP' established successfully
- After that I made a backup and added an interface:
Code Select
<opt4>
      <if>tun0</if>
      <descr>ipsec</descr>
      <enable>1</enable>
      <spoofmac/>
</opt4>
- Finally I have imported the backup (interface).
Then I have created a gateway under System-> Gateways-> Single

-Firewall->Rules->LAN configured

-Firewall->NAT-> Outbound Rule added

In the end, it was always indicated that the website is not secure.
Can anyone help?

