Menu

Show posts

This section allows you to view all posts made by this member. Note that you can only see posts made in areas you currently have access to.

Show posts Menu

Messages - tangofan

#1
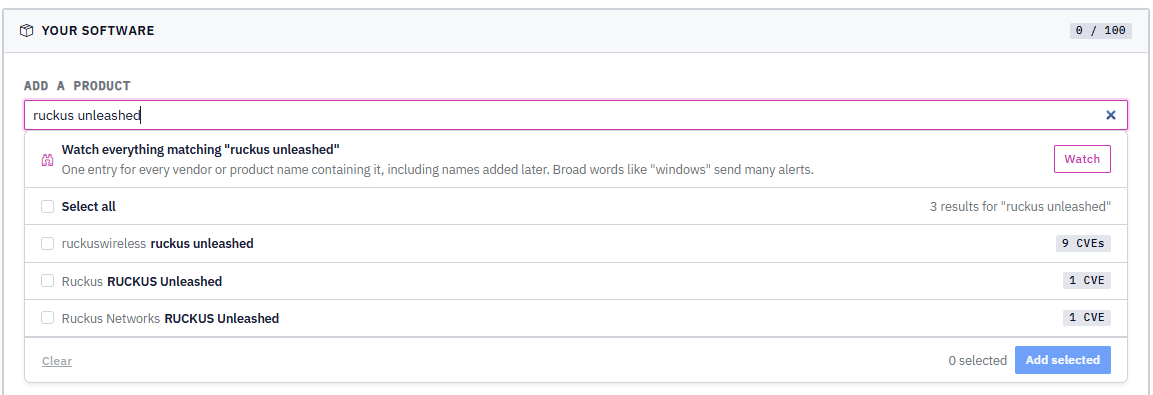
Quote from: Q-Feeds on November 05, 2026, 08:55:18 PMThat is indeed the intended use of the feature. It will then send you an alert whenever any product name contains "ruckus unleashed".
Thanks so much for the quick response, much appreciated.

It seems that the current search works like a phrase search. E.g. the search term "Ruckus Unleashed" does not find "Brocade Communications Systems, Inc.Ruckus Networks Unleashed APs and Zone Director". (I found that one just by searching for "unleashed".) It would be great, if in the future you could also provide "all words" match, so a term like the latter could also be found, so word order or additional words in-between don't matter.
#2
I am a Q-Feeds plus subscriber and am currently looking at the new CVE monitoring feature for paid subscribers.

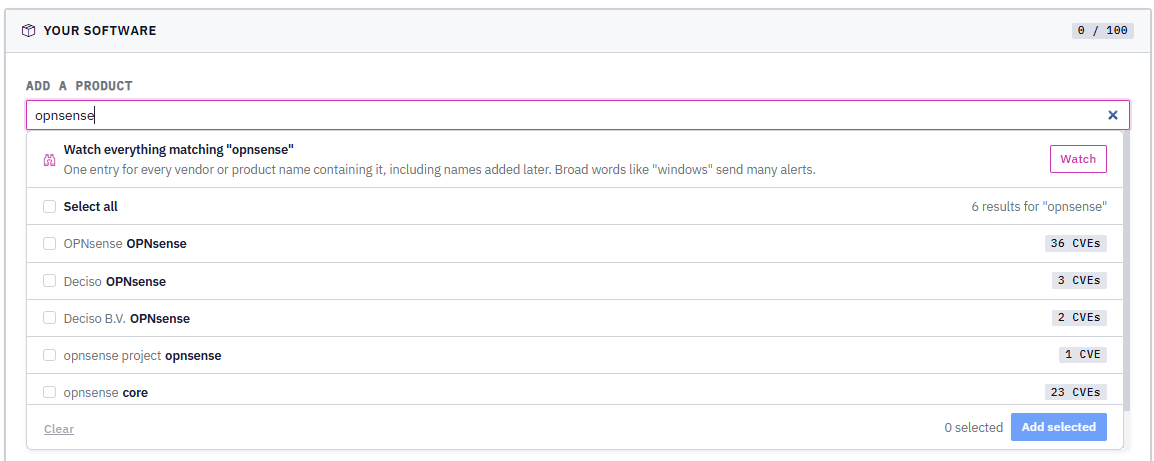
I checked for two products: OPNsense (of course!) and "Ruckus Unleashed", which is the "Unleashed" firmware for my Ruckus Wireless APs:


It seems like the product identification isn't curated and there are lots of variations for a single product name. (Understandably so BTW, I'm not complaining that it isn't curated.)

But given this state of affairs, would it be best just to select the "Watch everything matching ..." option, so I am sure to catch future variations of product names?
#3
German - Deutsch / Re: Performance verbessern
November 01, 2026, 08:51:22 AM
Falls du Zenarmor mit dem Emulated Netmap driver betreibst, sollte der Wechsel auf den Native Netmap driver noch etwas Geschwindigkeit herausholen. Ansonsten bin ich skeptisch, ob die Tunables etwas bringen, da die NICs ja anscheinend im Prinzip mit dem vollen Durchsatz laufen, sie werden halt durch Zenarmor im Single-Thread Modus ausgebremst. Du kannst natürlich mal im englischsprachigen Forum für Zenarmor nachfragen, ob da noch etwas geht.

Diese Tatsache (und ein gelegentliches Problem mit stotternden Videos in Youtube) hat letztendlich für mich den Ausschlag gegeben, Zenarmor zu deinstallieren, sogar bevor mein Premium-Abo abgelaufen war.
#4
German - Deutsch / Re: Performance verbessern
October 30, 2026, 06:55:32 PM
Wie ist die Performance bei dir denn jetzt und wie hast du sie gemessen?

Bei meinem System (Intel J6412 mit i226-V NICs) ist die inter-VLAN Performance von 1.1 Gbit/s auf ca. 2.4 Gbit/s gestiegen (gemessen mit iperf), nachdem ich Zenarmor abgeschaltet hatte. Da war dann keine weitere Optimierung mehr nötig. Zenarmor ist halt nur single-threaded (ausgenommen die ganz teueren Versionen), das wird dann dein Flaschenhals werden.

Ich habe übrigens alle Offloading Optionen unter Interface->Settings angekreuzt und damit deaktiviert. Mehr Performance würde das Offloading also nicht bringen, aber vielleicht weniger Stromverbrauch.
#5
According to the docs at https://docs.opnsense.org/manual/aliases.html you can indeed use fully-qualified domain names in aliases, though I haven't tried that myself.

I am not what the Crowdsec service has to do with your GeoIP problem and I can't really comment as to what's going on with CrowdSec, so I'll focus on the GeoIP problem.

Re. exceptions lists and changes to firewall rules: The firewall is stateful, so if you change certain rules (or aliases which affect rules) you might need to reset its state at Firewall: Diagnostics: States on the action tab. For good measure I usually click both button there.

Also your problem might be solved by setting your GeoIP firewall rule as an inbound rule on the WAN interface only and not on any of the LAN interfaces and VLANs. That way all your own actions, e.g. using a website in a blocked country still should work. (Don't forget to reset the firewall state after making the change.) If that doesn't help, you'll need to explain in greater detail, what scenario are you trying to cover with GeoIP and show your firewall rules.
#6
Quote from: franco on October 23, 2026, 10:44:52 AMTo be fair: Ad did all the work in the background this time.

> The release version didn't change, e.g. to 26.7.7_1.

This and the data installed on the firmware page not changing are intended in this out-of-band package update. Normally we try to avoid doing this, but the alleged severity left us little choice.

The PHP communication on this one seems a bit weird. Also dropping this at 14 UTC means 16 MEST so at the end of the work day. This also increased the pressure unnecessarily IMO.


Cheers,
Franco

Thanks for the background info, Franco. You all certainly did the right thing. I guess I was just a bit surprised, since I don't recall (in my 2+ years using OPNsense) having such an out-of-band update before. And for your and your colleagues' sake, I hope there won't be too many of them in the future.
#7
Quote from: iRobot on October 22, 2026, 09:19:16 AMHallo,
gefunden, es passiert bei jedem Update, auch bei dem aktuellen Update 26.7.1
In den iPv6-Einstellungen im LAN-Interface steht IPv6 Configuration Type auf "Identity association" und bei "Assign prefix ID" eine 10. Nach einem Update steht dort aber eine "0".
10 eintragen, speichern, schon läuft die FritzBox wieder als Telefonanlage.

Das wäre sicherlich einen Bugreport auf GitHub wert.
#8
Quote from: nero355 on October 21, 2026, 10:16:23 PMJust updated succesfully! Thanks to all the people involved getting this fixed soo fast! :)

Indeed, it was great to get a fix so quickly. One small nitpick: The release version didn't change, e.g. to 26.7.7_1. Perhaps just an oversight in the heat of battle. Certainly something that can be presumably easily corrected, if necessary.
#9
26.7, 26.10 Series / Re: DNS over TLS
October 17, 2026, 11:07:57 PM
Quote from: mika on October 17, 2026, 09:56:10 PMI also disabled the DNS server options.

In addition to what @meyergru said, I also suggest to be a bit more specific about the statement above, that is where did you change what exactly?
#10
Thanks to both of you for your suggestions. However I decided to uninstall ZenArmor about 3 weeks ago. My OPNsense box is a J6412 with 16GB of RAM and 2.5G NICs. The throughput between two VLANs was 1.1 Gb/s with ZenArmor enabled on those VLANs and ca. 2.4 Gb/s without it (measured with iperf). The stalling video was then the last straw and I decided to give up on ZenArmor.
#11
Quote from: Patrick M. Hausen on September 18, 2026, 11:36:36 PM
Quote from: tangofan on September 18, 2026, 09:44:58 PMPerhaps it would be a good idea, if at the time of uninstallation of a plugin, there was an option to erase the configuration block of that plugin

- System > Configuration > Defaults > Components
- Select "Services: ISC DHCPV4 [legacy] [dhcpd]"
- Click on "Reset"
- Repeat for DHCPV6

HTH,
Patrick

I was totally unaware that this feature even existed. OPNsense regularly surprises me on the positive side.

Many thanks, Patrick.
#12
Quote from: Remington on September 17, 2026, 10:32:57 PMFor me the issue seems to be an old DHCP/DHCPv6 configuration in config.yml which is not necessary anymore as I moved from ISC DHCP to DNSMASQ. I have created a backup of config.xml. Removed the <dhcp> and <dhcpv6> bock and restored the firewall from this config. This fixed the issue.
At the risk of derailing this thread ever so slightly: I used ISC before and switched to KEA not too long ago and - after looking at my config file for the first time ever - I also noticed a <dhcp> block. (Never had ipv6 active.)

Perhaps it would be a good idea, if at the time of uninstallation of a plugin, there was an option to erase the configuration block of that plugin, e.g. by having an additional popup querying, whether to erase that data. Obviously that would require additional entries in the metadata of each plugin as to where to find the configuration block(s). So if that additional metadata weren't present, that option to erase the config data wouldn't be available.
#13
26.7, 26.10 Series / Re: Firewall rules [new] missing
September 17, 2026, 09:17:37 PM
Quote from: SVMartin80 on September 17, 2026, 09:09:58 PMThanks both for the replies!

Patrick, if I understand correctly the version I'm currently running by default only shows the new rules and during an upgrade the rules already have been migrated automatically?

It totally makes sense to me that the new Rules page is now called 'Rules' and the legacy version is available through a plugin for users who prefer this.

However, what doesn't make sense to me is that I still see 'Migration assistant'; will that be removed soon in an update?
No, there is no automatic migration of the old rules. The new rules UI will show those old rules IIRC, but you can't edit them there. So you will need to go through the migration steps for your rules manually. IIRC the migration assistant "disappears", once everything is migrated.
#14
Quote from: stulpinger on September 17, 2026, 04:32:56 PMmein OPNsense ist auf 26.7.4_1
nur noch Rules im Menü 😎
Der "Rules [legacy]" Menüeintrag erscheint nur, wenn du das os-firewall-legacy Plugin installiert hast. Die Migration der alten Regeln ist aber auch ohne dieses Plugin möglich.
#15
General Discussion / Re: Block Local Network Connections?
September 16, 2026, 10:35:13 PM
Quote from: lmoore on September 16, 2026, 01:29:21 AMI don't have a Smart TV for privacy reasons. However, any device used to stream content from the Internet can send telemetry.

Reading this article, NTP is also utilised for gathering information.

I've included a Destination NAT rule to redirect NTP connections to OPNsense.

I found that I also needed an SNAT rule for NTP, so my Synology NAS would accept the response from the OPNsense NTP server. Other clients might require the same.